Web Application
Penetration
Testing
Expert-led testing for web apps and SaaS platforms to find security flaws, validate findings, and track fixes in one platform.
- CREST accredited
- OWASP WSTG
- OWASP ASVS
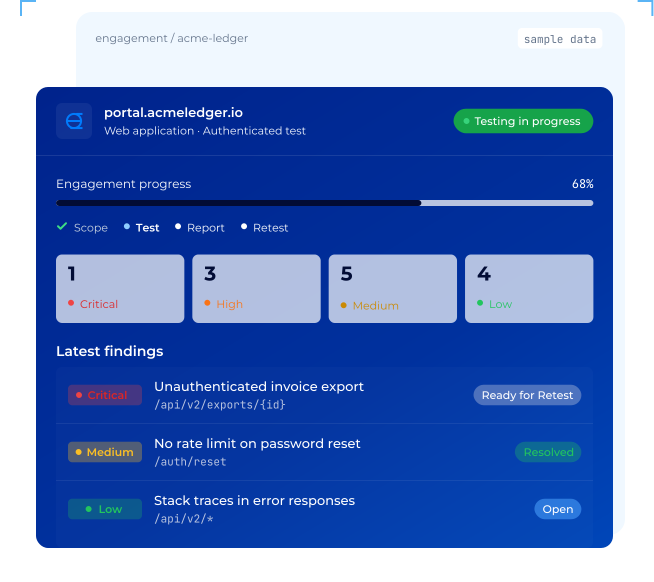
- What We Test
Comprehensive testing
across your web application.
Our specialists assess critical security controls and business workflows using the OWASP Web Security Testing Guide, with testing tailored to your application's architecture and risk profile.
- WSTG-ATHN••••••••bypass?
Authentication
Assess login, MFA, password reset and account recovery for weaknesses that could enable unauthorised access.
- WSTG-ATHZREADEDITDELadmineditorviewer
Authorisation & access control
Test whether user roles, permissions and tenant boundaries are enforced across application workflows.
- WSTG-SESSissuedrefreshedlogoutstill valid
Session management
Assess session creation, expiration, invalidation and token handling to identify session security weaknesses.
- WSTG-BUSL1 cart2 pay3 confirmstep 2 skipped
Business logic
Identify ways application workflows, transactions and business rules could be manipulated or bypassed.
- WSTG-INPV' OR 1=1--query()all rows
Injection & input handling
Test how applications handle untrusted input across queries, templates and browser interactions.
- WSTG-CONF
- HSTS✓ set
- CSP✗ missing
- X-Frame-Options✓ set
Security configuration
Assess security headers, transport protections, error handling and relevant application configuration weaknesses.
- How We Test
Five steps, one team, from scope to retest.
Work directly with experienced pentesters throughout your engagement, with testing, findings and remediation managed through one connected platform.
- 01
Scope
Agree testing objectives, application boundaries, access requirements and rules of engagement.
- 02
Test
Specialists conduct hands-on testing of your application's security controls and business logic.
- 03
Review
Receive human-validated findings with severity ratings, technical evidence and remediation guidance.
- 04
Remediate
Work directly with your pentesters to understand and address vulnerabilities.
- 05
Retest
Verify fixes through retesting and record the outcome within your agreed engagement terms.
Specialist-led delivery
- LP
Your Testing Lead
A clear point of contact throughout the engagement.
- WEB
Security Specialists
Hands-on assessment of security controls and business logic.
- QA
Technical Quality Review
Validation and review of findings before reporting.
Ready to scope your web application?
Discuss your requirements with our specialists and define the right testing approach for your environment.
- What You Receive
Findings you can act on, and proof they're fixed.
Web App pentest report
SAMPLE- CriticalIDOR on /invoices/{id}CVSS 9.1
- HighStored XSS in commentsCVSS 7.4
- MediumNo rate limit on resetCVSS 5.3
Technical & Executive Reporting
Access human-validated findings, technical evidence and remediation guidance through the CTB platform, with detailed reports for engineering teams and security leadership.
GET /api/invoices/1043
# session: user-a (tenant A)
200 OK · tenant-b invoice returned
Reproducible evidence
Clear reproduction steps, requests and responses help engineers understand and resolve each vulnerability.
Verified Retesting
Request retesting once fixes are ready and track their verification status through the platform, within agreed engagement terms.
“Capture The Bug's continuous pentesting approach has been a game-changer for us at LawVu.”
Sarah Webb
Chief Operating Officer, LawVu
We'll agree on the application scope, testing objectives, environment, user roles and access requirements. Our specialists guide you through onboarding and the necessary test accounts.
Yes. Our experienced pentesters conduct hands-on assessments of your application's security controls, business logic and access boundaries, supported by established testing methodologies and security tools.
Findings are manually validated and reviewed before reporting.
Yes, where production testing is appropriate and authorised. We agree on the scope, testing windows, access controls and rules of engagement in advance, with safeguards to minimise operational disruption.
Where appropriate, testing can also be conducted in staging environments.
Pricing depends on application complexity, functionality, user roles, integrations, testing access and the agreed scope.
We provide a written proposal outlining the assessment approach, deliverables and costs.
Yes. Retesting is included within your agreed engagement terms. Once your team addresses a finding, our specialists verify the remediation and document the result through the Capture The Bug platform.
Ready to test your web application?
Discuss your security requirements with our specialists. We'll help define the scope, testing approach and deliverables for your environment.