API Penetration
Testing
Expert-led testing of REST, GraphQL and partner APIs. Uncover exploitable access control and business logic vulnerabilities, with validated findings and verified remediation.
- CREST accredited
- OWASP API Top 10
- OWASP ASVS

- What We Test
Six critical areas of API
security testing.
Testing is aligned with the OWASP API Security Top 10 (2023) and tailored to your API architecture.
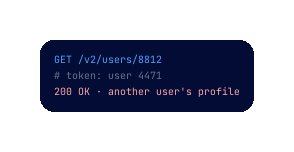
- API1:2023
GET /v2/users/8812
# token: user 4471
200 OK · other user's data
Object-Level Authorisation
Test whether users can access API objects beyond their permissions.
- API2:2023
{ "alg": "none",
"sub": "4471",
"exp": 1893456000 }
Authentication
Assess token security, authentication flows and session handling.
- API3:2023
PATCH /v2/me
{ "name": "Alex",
"role": "admin" }
Property-Level Authorisation
Identify fields users can access or modify without authorisation.
- API4:2023POST /otp5,000 req/min
limit not enforced
Resource Consumption
Assess rate limiting, resource exhaustion and abusive API usage.
- API5:2023GETPUTADMuseradmin
Function-Level Authorisation
Test whether users can invoke restricted administrative or business functions.
- API6:2023signuppromo ×500credit
Sensitive Business Flows
Identify workflows vulnerable to automation, abuse or manipulation.
- How We Test
Five steps, one team, from scope to retest.
Work directly with experienced API security specialists throughout testing, remediation and retesting, through one connected platform.
- 01
Scope
Agree API endpoints, user roles, access requirements and testing boundaries.
- 02
Test
Assess authorisation, authentication, data exposure and API business logic.
- 03
Review
Receive validated findings with severity ratings and technical evidence.
- 04
Remediate
Collaborate with pentesters to address vulnerabilities and implement fixes.
- 05
Retest
Verify remediation and document results within agreed engagement terms.
Your assigned specialists
- LP
Testing Lead
Your named point of contact throughout the engagement.
- API
API Security Specialist
Expertise in authorisation, API workflows and business logic.
- QA
Technical Quality Review
Findings reviewed for technical accuracy and reproducibility.
Ready to scope your API test?
Discuss your API architecture and security requirements with our specialists.
- What You Receive
Findings you can act on, and proof they're fixed.
API pentest report
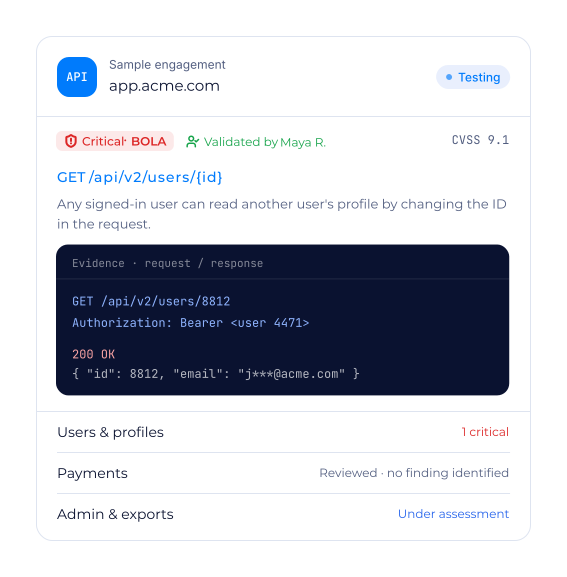
SAMPLE- CriticalBOLA on /invoices/{id}CVSS 9.1
- HighMass assignment on /usersCVSS 7.4
- MediumNo rate limit on /loginCVSS 5.3
Technical & Executive Reporting
Access validated findings, technical evidence and remediation guidance through one platform, with detailed reports for engineering teams and security leadership.
GET /api/invoices/1043
# session: user-a (tenant A)
200 OK · tenant-b invoice returned
Reproducible Evidence
Clear API requests, responses and reproduction steps help engineers understand and resolve vulnerabilities.
Verified Retesting
Request retesting when fixes are ready and track verified outcomes through the platform, within agreed engagement terms.
“The platform made it easy to scope, schedule, and track the test in real time-no long email chains or delays.”
Shai Bhula
Chief Technology Officer, Whip Around
We test REST, GraphQL, gRPC and WebSocket APIs, including partner integrations and open banking environments.
We typically need API documentation, endpoint details, test credentials, user roles and access to an agreed testing environment. Our specialists guide you through scoping and onboarding.
Yes. Our specialists assess API functionality, identify accessible endpoints and test authorisation boundaries, business logic and multi-step workflows. Testing depth depends on the agreed scope and access.
Pricing depends on API complexity, endpoint coverage, authentication methods, user roles, integrations and testing requirements. We provide a tailored proposal outlining the scope, methodology and deliverables.
Once your team has addressed the findings, our specialists retest the relevant vulnerabilities and document the results through the CTB platform. Retesting is included within your agreed engagement terms.
Ready to test your API?
Discuss your API architecture and security requirements with our specialists. We'll define the testing scope, methodology and deliverables for your environment.