Mobile App
Penetration
Testing
Expert-led testing of iOS and Android applications and their APIs. Identify exploitable vulnerabilities in authentication, data storage, application logic and backend security.
- CREST accredited
- OWASP MASVS
- OWASP MASTG

- What We Test
Six critical areas of mobile
security testing.
Testing is guided by OWASP MASVS and MASTG, tailored to your application's architecture and risk profile.
- MASVS-STORAGEtoken.txt
Data Storage
Assess sensitive data, credentials and tokens stored on the device.
- MASVS-CRYPTO
- AES-GCM✓ ok
- Hardcoded key✗ found
- Keystore✓ ok
Cryptography
Evaluate encryption, key management and cryptographic implementation.
- MASVS-AUTH•••••••••bypass?Biometric
Authentication
Test login, biometric authentication and session security.
- MASVS-NETWORKMITMapi.acme.com
Network Communication
Assess TLS protections, certificate validation and API traffic.
- MASVS-PLATFORM
# deep link
acme://transfer
?to=attacker&amt=500
Platform Interaction
Test deep links, WebViews, permissions and inter-app communication.
- MASVS-RESILIENCE
- Root detection✗ bypassed
- Hook detection✗ bypassed
- Tamper check✓ held
Resilience
Assess protections against tampering, reverse engineering and runtime manipulation.
- How We Test
Five steps, one team, from scope to retest.
Work directly with experienced mobile security specialists throughout testing, remediation and retesting, through one connected platform.
- 01
Scope
Agree app versions, platforms, test accounts and assessment boundaries.
- 02
Test
Assess mobile security controls, runtime behaviour and backend APIs.
- 03
Review
Access validated findings with severity ratings and technical evidence.
- 04
Remediate
Collaborate with pentesters to address vulnerabilities and implement fixes.
- 05
Retest
Verify remediation and document results within agreed engagement terms.
Your assigned specialists
- LP
Testing Lead
Your named point of contact.
- MOB
Mobile Security Specialist
Expertise in iOS, Android and runtime security.
- QA
Technical Quality Review
Findings reviewed for accuracy and reproducibility.
Ready to scope your mobile app test?
Discuss your mobile application and security requirements with our specialists.
- What You Receive
Findings you can act on, and proof they're fixed.
Mobile pentest report
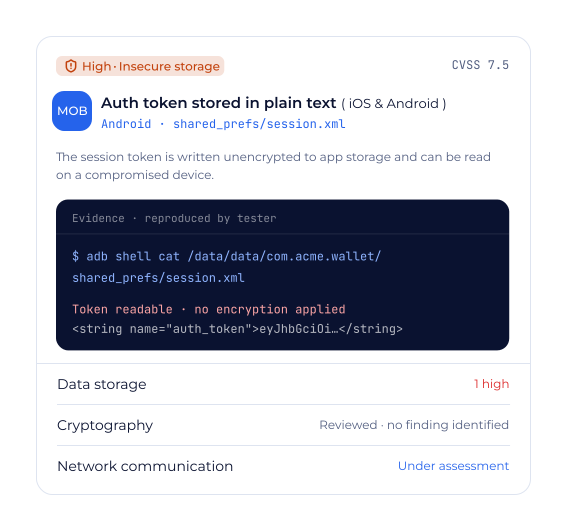
SAMPLE- HighTokens stored in plaintextCVSS 8.0
- HighCertificate pinning bypassedCVSS 7.7
- MediumExported activity without authCVSS 5.0
Technical & Executive Reporting
Access validated mobile security findings, technical evidence and remediation guidance through one platform, with detailed reports for engineering teams and security leadership.
adb shell cat shared_prefs/session.xml
# app data on rooted device
token: eyJhbGci… · plaintext
Reproducible Evidence
Clear reproduction steps, device details and technical evidence help engineers understand and resolve mobile application vulnerabilities.
Verified Retesting
Request retesting once fixes are ready and track verified remediation through the platform, within agreed engagement terms.
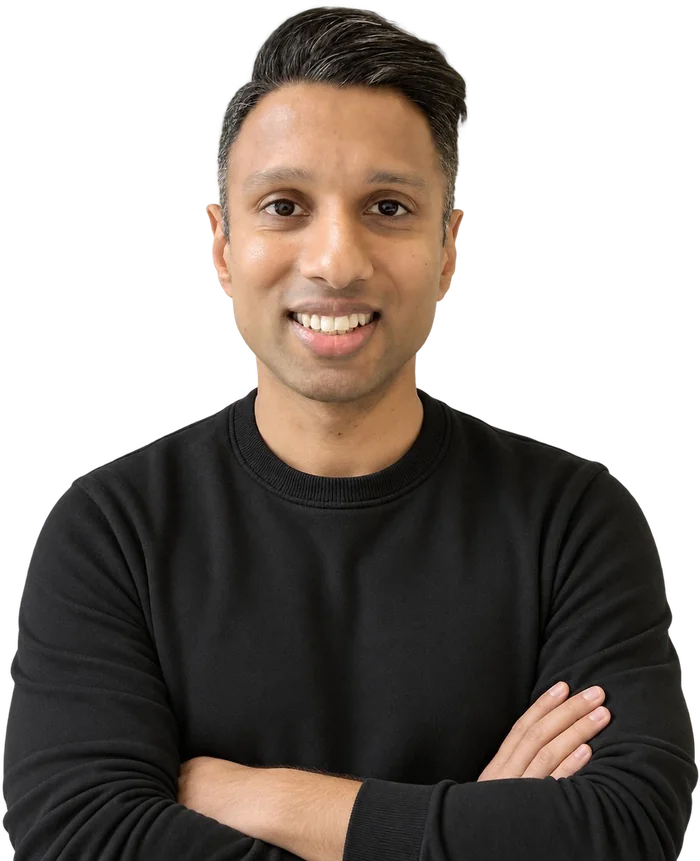
“The platform made it easy to scope, schedule, and track the test in real time-no long email chains or delays.”
Shai Bhula
Chief Technology Officer, Whip Around
Yes. We assess native iOS and Android applications, including React Native and Flutter apps, along with supporting backend APIs where included in scope.
Not always. We offer black-box and grey-box mobile penetration testing. Access to source code, architecture documentation and test credentials can support deeper analysis, depending on the assessment requirements.
Yes. We assess authentication, authorisation, data exposure and business logic across mobile backend APIs, where included in the agreed testing scope.
Pricing depends on the number of applications, supported platforms, functionality, user roles, backend APIs and testing complexity. We provide a tailored proposal outlining the assessment scope, methodology and deliverables.
Once your team has addressed the findings, our specialists retest the relevant vulnerabilities and document the results through the CTB platform. Retesting is included within your agreed engagement terms.
Ready to test your mobile app?
Discuss your application architecture and security requirements with our specialists. We'll help define the testing scope, methodology and deliverables for your assessment.