Cloud Penetration
Testing
Expert-led penetration testing for AWS, Azure and Google Cloud. Identify exploitable misconfigurations, privilege escalation and attack paths across your cloud environments.
- CREST-Accredited Provider
- CIS Benchmarks-Informed Testing
- AWS / Azure / Google Cloud

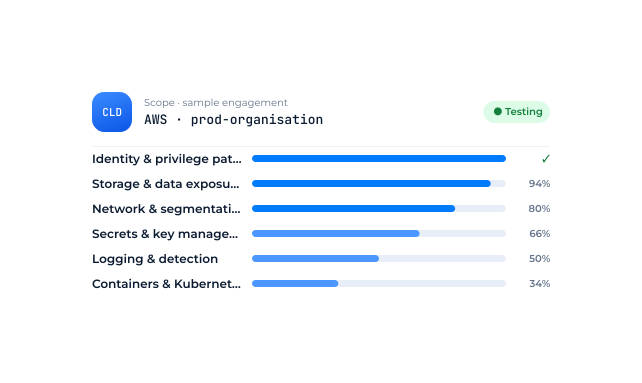
- What We Test
Six critical areas of cloud
security testing.
We combine CIS Benchmarks-informed configuration reviews with hands-on testing of exploitable cloud attack paths.
- IAMdev-roleiam:PassRoleadmin
Identity & Privilege Paths
Assess IAM roles, permissions and potential privilege escalation.
- DATAexportspublic read · 1,204 files
Storage & Data Exposure
Identify exposed storage, databases and sensitive cloud data.
- NET
# security group
port 22 · ssh
source 0.0.0.0/0
Network & Segmentation
Test network controls, isolation boundaries and exposed services.
- KMS
# config.yml
db_host: prod-db
db_pass: Sup3r…
Secrets & Key Management
Assess exposed credentials, tokens and secrets handling.
- LOG2 events not logged09:0209:0509:0709:09
Logging & Detection
Evaluate security event visibility, alerting and detection controls.
- K8Sprivileged pod
Containers & Kubernetes
Assess cluster permissions, workload isolation and container security.
- How We Test
Five steps, one team, from scope to retest.
Work directly with experienced cloud security specialists throughout testing, remediation and retesting, through one connected platform.
- 01
Scope
Agree cloud accounts, environments, permissions and testing boundaries.
- 02
Test
Assess cloud misconfigurations, identity permissions and exploitable attack paths.
- 03
Review
Receive validated findings with severity ratings and technical evidence.
- 04
Remediate
Collaborate directly with specialists to address identified cloud security risks.
- 05
Retest
Verify fixes and document remediation within agreed engagement terms.
Your assigned specialists
- LP
Testing Lead
Your named point of contact.
- CLD
Cloud Security Specialist
Expertise in IAM, cloud configuration and attack paths.
- QA
Technical Quality Review
Findings reviewed for accuracy and reproducibility.
Ready to scope your cloud assessment?
Discuss your cloud environment and security requirements with our specialists.
- What You Receive
Findings you can act on, and proof they're fixed.
Cloud pentest report
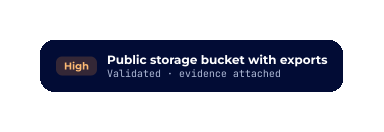
SAMPLE- HighPublic bucket with exportsCVSS 8.0
- HighRole allows iam:PassRoleCVSS 7.7
- MediumCloudTrail not multi-regionCVSS 5.0
Technical & Executive Reporting
Access human-validated cloud security findings, technical evidence and remediation guidance through one platform, with detailed reports for engineering teams and security leadership.
aws s3 ls s3://acme-exports --no-sign-request
# anonymous access
listed 1,204 objects · public read
Reproducible Evidence
Clear evidence of cloud misconfigurations, permissions and attack paths, with steps your engineers can reproduce and verify.
Verified Retesting
Request retesting once fixes are ready and track verified remediation through the platform, within agreed engagement terms.
“As a leading Kubernetes company, we understand the importance of securing our data and systems. Their ethical hackers provided a thorough security assessment, with clear and concise reporting that included actionable recommendations.”
Robbie Gill
Vice President of Engineering, Rafay Systems
We assess AWS, Microsoft Azure and Google Cloud environments, including Kubernetes clusters and containerised workloads. Testing is tailored to your cloud architecture, services and security requirements.
Access depends on the agreed scope. We may require read-only access for configuration reviews and explicitly authorised test permissions for hands-on assessments. Our specialists agree on access requirements and testing boundaries before starting.
Both approaches may form part of an engagement. Configuration reviews assess settings, identity controls and security posture, while penetration testing examines how weaknesses can be exploited or combined into realistic attack paths.
We tailor the assessment to your environment and security objectives.
Pricing depends on cloud architecture, number of accounts or subscriptions, services in scope, testing complexity and access requirements.
We provide a tailored proposal outlining the assessment scope, methodology, deliverables and costs.
Once your team has addressed a finding, our specialists retest the relevant security controls or attack paths and document the outcome through the Capture The Bug platform.
Retesting is included within your agreed engagement terms.
Ready to test your cloud?
Discuss your cloud environment and security requirements with our specialists. We'll define the testing scope, methodology and deliverables for your assessment.