Network
Penetration
Testing
Expert-led testing of external and internal networks. Uncover exploitable vulnerabilities, privilege escalation and lateral movement risks, with validated findings and remediation guidance.
- CREST-Accredited Provider
- NIST SP 800-115-Informed
- PTES-Aligned

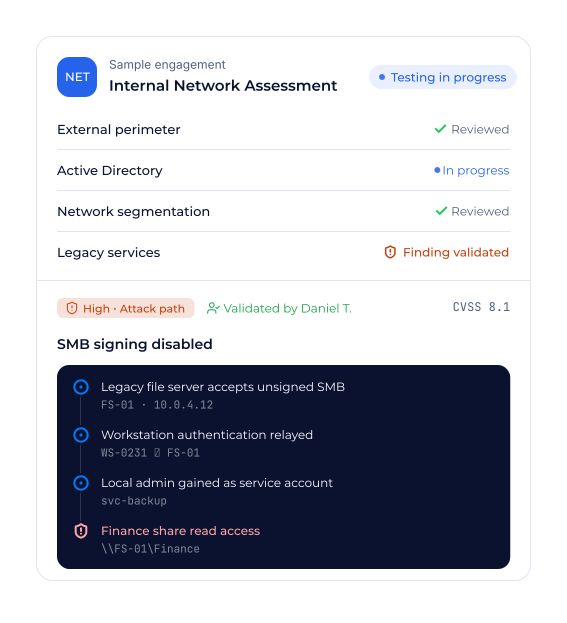
- What We Test
Six areas we test
across your network.
Our specialists assess exploitable network weaknesses and attack paths using recognised methodologies, tailored to your environment and agreed scope.
- EXTinternetfirewallvpn.acme
External Perimeter
Assess internet-facing hosts, exposed services and remote access security.
- INTlaptopfileserverdb01
Internal Network
Identify exploitable weaknesses and potential lateral movement paths.
- SEGreachableofficepayments
Network Segmentation
Test isolation controls and access between sensitive network zones.
- ADDomain Adminssvc_backupuser01
Active Directory
Assess privilege escalation paths, weak configurations and domain security.
- WLANreachableguestcorp
Wireless Security
Test Wi-Fi access controls, network isolation and wireless security.
- SVC
- 21/ftp✗ anon
- 22/ssh✓ ok
- 445/smb✗ open
Exposed & Legacy Services
Identify outdated services, insecure configurations and unnecessary exposure.
- How We Test
Five steps, one team, from scope to retest.
The same specialists stay with your network test from the first call to the final retest.
- 01
Scope
Agree network ranges, access requirements, testing objectives and boundaries.
- 02
Test
Assess exposed services, network weaknesses and potential attack paths.
- 03
Review
Receive validated findings with severity ratings and technical evidence.
- 04
Remediate
Collaborate directly with pentesters to address network security weaknesses.
- 05
Retest
Verify remediation and document outcomes within agreed engagement terms.
Your assigned specialists
- LP
Testing Lead
Your named point of contact.
- NET
Infrastructure Security Specialist
Expertise in external networks, Active Directory and lateral movement.
- QA
Technical Quality Review
Findings reviewed for accuracy and reproducibility.
Ready to scope your network test?
Discuss your infrastructure and security requirements with our specialists.
- What You Receive
Findings you can act on, and proof they're fixed.
Network pentest report
SAMPLE- HighSMB signing disabledCVSS 7.5
- HighKerberoastable service accountCVSS 7.2
- MediumTLS 1.0 on VPN gatewayCVSS 5.9
Technical & Executive Reporting
Access validated network security findings, technical evidence and remediation guidance through one platform, with detailed reports for technical teams and security leadership.
nmap -sV 203.0.113.12
# 445/tcp open microsoft-ds
smb signing: disabled (relay possible)
Reproducible Evidence
Clear evidence of exposed services, security weaknesses and attack paths, with technical steps to help your team reproduce and resolve findings.
Verified Retesting
Request retesting once fixes are ready and track verified remediation through the platform, within agreed engagement terms.
“The workflow overall feels far more natural and is much better aligned with our delivery cadence – and provides learning opportunities for our team at the same time.”
Jan Behrens
Chief Technical & Product Officer, Devoli
External testing assesses internet-facing systems and services that attackers could access remotely. Internal testing evaluates security weaknesses, privilege escalation and lateral movement risks from within your network.
Not always. External assessments can typically be performed remotely. Internal testing may be conducted through secure remote access or on-site, depending on your infrastructure, security requirements and agreed scope.
Testing is conducted within agreed rules of engagement, including authorised targets, testing windows and escalation procedures. Our specialists take precautions to minimise disruption, with potentially intrusive testing coordinated in advance.
Pricing depends on the number of IP addresses, network segments, locations, testing objectives and the complexity of your environment.
We provide a tailored proposal outlining the assessment scope, methodology, deliverables and costs.
Yes. We assess Active Directory security, including account permissions, privilege escalation paths, authentication weaknesses and misconfigurations that could expose sensitive systems or enable lateral movement.
Ready to test your network?
Discuss your network infrastructure and security requirements with our specialists. We'll define the testing scope, methodology and deliverables for your environment.