Tenant Isolation
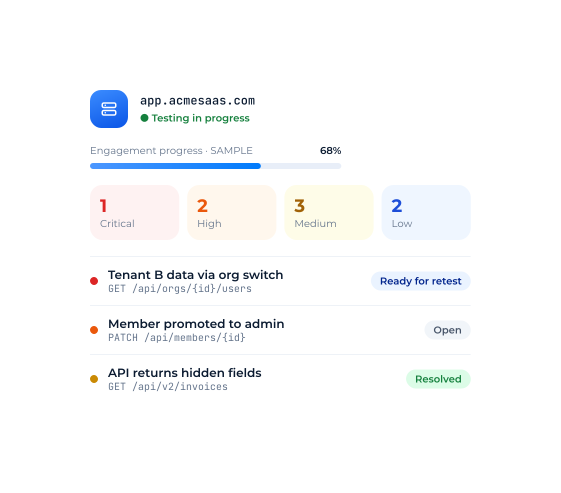
Weak tenant isolation exposes customer data across shared SaaS environments.
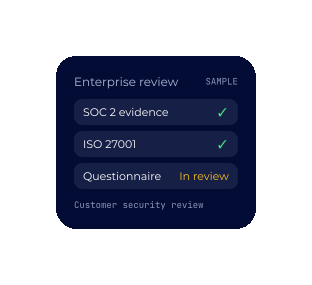
Expert testing for multi-tenant apps, APIs and cloud environments, with evidence for SOC 2, ISO 27001 and customer security reviews.

“We would highly recommend Capture The Bug to anyone who needs continuous assurance and speed without compromising depth.”
Independent Assurance
 CREST-Accredited
- SaaS Risks
Four risks enterprise security teams expect you to test.
Weak tenant isolation exposes customer data across shared SaaS environments.
Weak role controls enable unauthorised access to administrative functions.
API responses exposing sensitive fields beyond intended application access controls.
Excessive cloud permissions and credentials expand access beyond intended boundaries.
- What We Test
Multi-tenant applications and administrative consoles.
Learn morePublic, private and integration APIs.
Learn moreAWS, Azure and Google Cloud environments.
Learn moreAI agents embedded within SaaS products.
Learn moreCompanion mobile applications and workflows.
Learn moreCorporate and hybrid network environments.
Learn more- How We Work
Expert-led testing, live findings and remediation tracking throughout your SaaS programme.
Define tenant boundaries, user roles and testing requirements.
Agreed ScopeSpecialists assess SaaS applications for exploitable weaknesses.
Live FindingsValidated findings include evidence, severity and remediation guidance.
Validated FindingsCollaborate with specialists to resolve vulnerabilities across your platform.
Fix GuidanceRetest fixes within agreed engagement terms.
Verified FixDiscuss your testing scope and priorities with our security specialists.
- Assurance & Evidence
SOC 2
Validated findings supporting relevant security controls.
ISO 27001
Technical evidence supporting information security management.
OWASP ASVS
Security testing aligned with recognised application verification standards.
Customer Security Reviews
Reports supporting enterprise customer security assessments.
Validated findings and remediation evidence support enterprise security reviews, customer assurance and compliance requirements.
Our reports provide validated findings and testing evidence for your auditor to review. We can align scope with their requirements before testing begins, where appropriate.
Yes. We assess whether users can access another organisation's data, resources or administrative functions through weaknesses in tenant isolation and authorisation controls.
Yes. Our continuous penetration testing programmes can align with your release cadence, prioritising new features, changing APIs and security-critical functionality within the agreed scope.
Our reports provide technical findings, severity ratings and remediation evidence for customer security reviews. Acceptance depends on each customer's requirements and procurement process.
Once your team implements fixes, our specialists retest affected functionality and document verification outcomes through the CTB platform, within your agreed engagement terms.
Expert-led penetration testing for growing enterprise SaaS platforms.