Access Across Matters and Clients
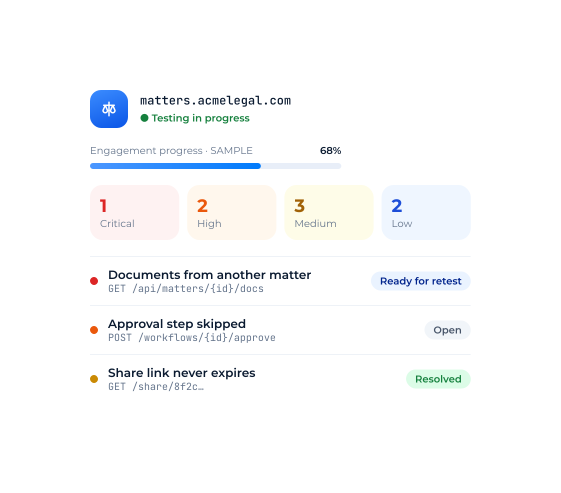
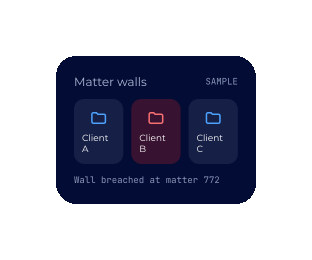
Broken access controls exposing confidential documents across clients and matters.
Expert-led penetration testing for legal platforms, confidential documents and client portals, with validated findings and verified remediation through our platform.

“Security and trust are essential when building a platform that helps organisations manage procurement and compliance. Capture The Bug has made penetration testing a more collaborative and transparent process for our team. Having direct access to their pentesters, clear visibility of findings and a straightforward approach to remediation helps us address risks efficiently while continuing to develop and improve our platform.”
Independent Assurance
 CREST-Accredited Testing
- Legal Tech Risks
Four security weaknesses that expose sensitive legal and client information.
Broken access controls exposing confidential documents across clients and matters.
Malicious documents exploiting weaknesses in file processing and preview services.
Authorisation weaknesses allowing documents to bypass required approval steps.
Insecure links exposing confidential documents beyond intended recipients and permissions.
- What We Test
Legal, contract and compliance platforms.
Learn moreDocument, matter and integration APIs.
Learn moreApplications for lawyers, clients and approvers.
Learn moreSecure document storage and processing environments.
Learn moreLegal research and contract analysis assistants.
Learn moreLaw firm and office networks.
Learn more- How We Work
Expert-led testing, live findings and specialist collaboration throughout your security assessment.
Agree matter access, user roles and testing boundaries.
Agreed ScopeTest document access, workflows and exploitable vulnerabilities.
Live FindingsReview validated findings, evidence, severity and remediation guidance.
Validated FindingsCollaborate directly with specialists to address risks in workflows.
Fix GuidanceVerify fixes within agreed engagement terms.
Verified FixDiscuss confidential workflows and security testing needs with our specialists.
- Assurance & Evidence
ISO 27001
Technical evidence supporting information security management controls.
SOC 2
Findings supporting relevant security control reviews.
Privacy Act
Testing evidence supporting protection of confidential client and personal information.
Client Security Reviews
Reports supporting your clients' security assurance reviews.
Validated findings and retesting evidence support client assurance, security reviews and relevant compliance requirements.
Yes. We assess authorisation controls to identify whether users can access confidential documents beyond their assigned permissions.
Yes. We assess file uploads, document parsing and preview functionality for exploitable vulnerabilities within agreed testing scope.
Yes. Our reports provide validated findings, technical evidence and remediation outcomes supporting client security reviews and audits.
Yes. We assess AI assistants, document retrieval and tool permissions for unauthorised access and sensitive data exposure.
Once your team implements fixes, our specialists verify remediation and document outcomes through the CTB platform.
Expert-led penetration testing for confidential legal technology platforms.