Checkout & Pricing Logic
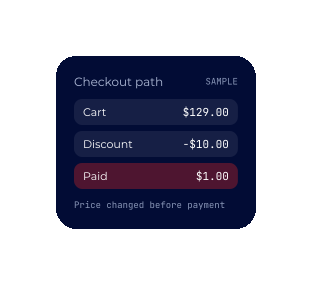
Manipulated prices, discounts and gift cards affecting transaction integrity.
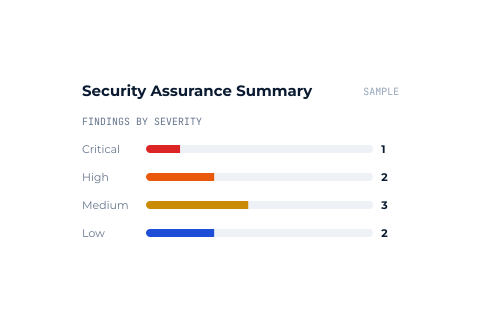
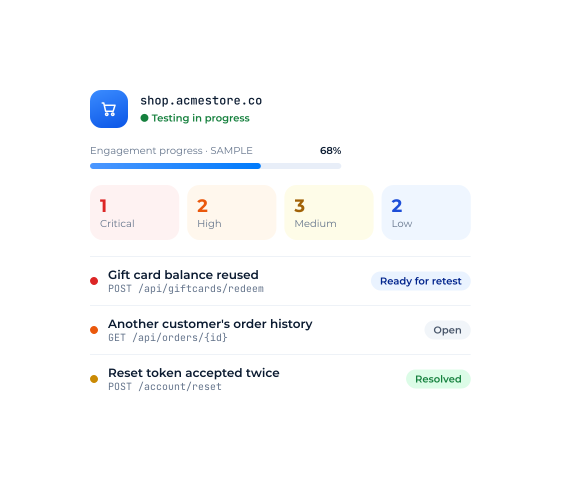
Expert-led testing for checkout flows, customer accounts, payment APIs and integrations, with validated findings and verified remediation.

“What we value about Capture The Bug is the flexibility to align security testing with how our team builds and releases software. Having visibility into findings, direct access to pentesters and a clear remediation process makes security testing much easier to manage.”
Independent Assurance
 CREST-Accredited Penetration Testing
- Commerce Security Risks
Four critical security risks across modern commerce platforms.
Manipulated prices, discounts and gift cards affecting transaction integrity.
Authentication and recovery weaknesses enabling unauthorised account access.
Broken access controls exposing customer orders and sensitive information.
Compromised scripts and plugins exposing payment or customer data.
- What We Test
Storefronts, checkout workflows and customer accounts.
Learn moreCart, order, inventory and payment APIs.
Learn moreShopping, loyalty and mobile payment applications.
Learn moreCloud infrastructure supporting commerce and payments.
Learn moreAI shopping assistants and connected business tools.
Learn moreRetail infrastructure, store networks and segmentation.
Learn more- How We Work
Expert-led testing with live findings, direct specialist collaboration and remediation tracking through one connected platform.
Agree commerce applications, payment flows, user roles and testing boundaries.
Agreed ScopeAssess checkout logic, account security, APIs and exploitable vulnerabilities.
Live FindingsAccess validated findings with technical evidence, severity ratings and remediation guidance.
Validated FindingsWork directly with specialists to address risks across commerce workflows.
Fix GuidanceVerify remediation and document outcomes within agreed engagement terms.
Verified FixesDiscuss your testing requirements and security priorities with our specialists.
- Assurance & Evidence
PCI DSS v4.0.1
Penetration testing evidence for applicable requirements.
Payment Page Security
Testing evidence supporting checkout and third-party script security.
Privacy Act 2020
Security evidence supporting customer data protection.
SOC 2
Validated findings supporting relevant security controls.
Validated findings, technical evidence and verified fixes support customer assurance, risk management and relevant compliance requirements.
Testing is planned around your operational requirements, with agreed testing windows and safeguards to minimise disruption. Potentially disruptive activities are coordinated separately, particularly during critical trading periods.
Yes. Our specialists assess checkout workflows, promotion rules, loyalty programmes and gift card functionality for business logic weaknesses that could enable unauthorised transactions or financial abuse.
Yes. We assess third-party integrations and payment-page security within the agreed scope, including exposed APIs, insecure configurations and risks associated with externally loaded scripts.
Yes. We can scope penetration testing to support applicable PCI DSS requirements, including Requirement 11.4. Our specialists can align testing objectives and reporting with your compliance programme and QSA, where applicable.
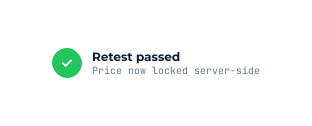
Once your team has addressed a vulnerability, our specialists retest the affected functionality and document the outcome through the CTB platform, within agreed engagement terms.
Expert-led penetration testing for evolving commerce platforms.