Is Annual Pentesting Enough for SaaS?
Your product changes every week, but your pentest happens once a year. Learn how to close the gap between the two.
WHAT YOU’LL LEARN
- What an annual pentest is designed to prove, and what it cannot
- The signs your testing isn’t keeping up with your releases
- How mature SaaS teams extend annual testing with targeted tests
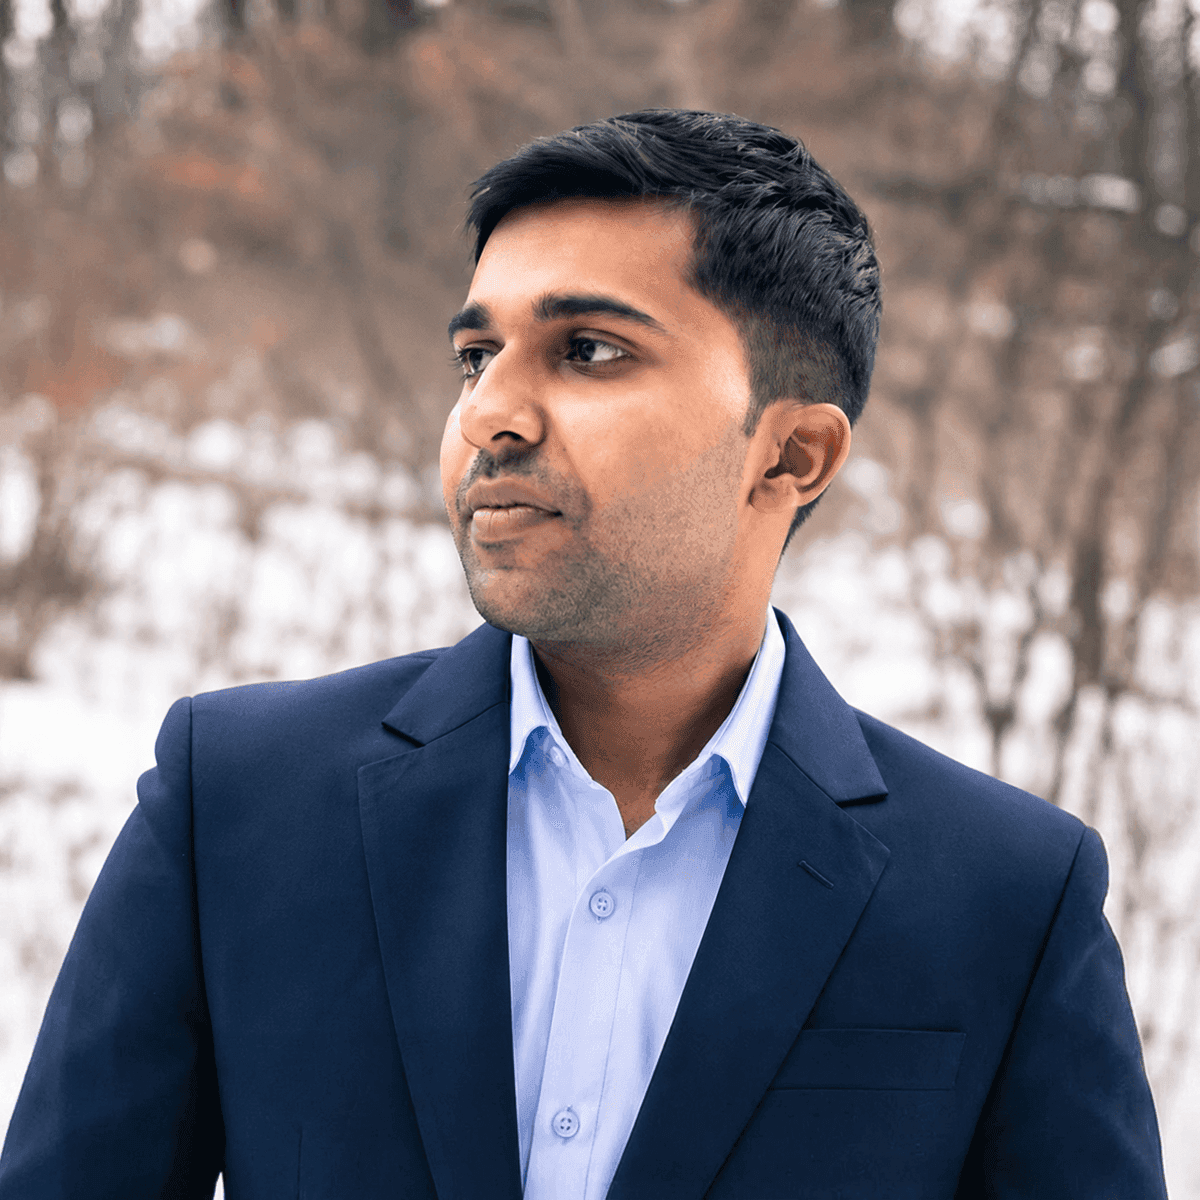
Written by Capture The Bug specialists
Jitendra Kumar Singh, Associate Director & Pentester
eWPTX-certified pentester at Capture The Bug, securing web apps, APIs and networks one vulnerability at a time.
 CREST-Accredited
 CREST-Accredited AI Testing
TRUSTED BY SECURITY-CONSCIOUS TECHNOLOGY TEAMS
- Inside the Guide
Four chapters on testing
at SaaS speed.
Practical guidance for keeping security testing in step with how often you ship.
What annual pentesting is designed to do
How an annual test validates your controls and finds exploitable vulnerabilities, and why it still matters.
Why fast-moving SaaS creates testing gaps
Deployments, API changes, integrations and cloud updates add new risk between annual tests.
When annual testing alone is not enough
The signs that security testing isn’t keeping pace with your release cycle.
How mature SaaS teams approach testing
Extending annual pentesting with targeted testing and ongoing visibility.
THE EXPOSURE WINDOW
One test a year. Fifty-two release weeks.
- Who It’s For
Written for the people who
own the decision.
Security leaders and CISOs
Decide when an annual test is enough, and when it leaves you exposed.
CTOs and engineering leaders
Align security testing with how often your team actually ships.
Risk, compliance and procurement teams
Understand what an annual report does and does not prove to customers and auditors.